Security / Privacy / Tor
Whonix Patches IPv6 Leak That Could Expose Users Outside Tor
Whonix patched an IPv6 leak that could bypass Tor from a compromised Workstation. Check affected setups, firewall versions and the steps to update safely.
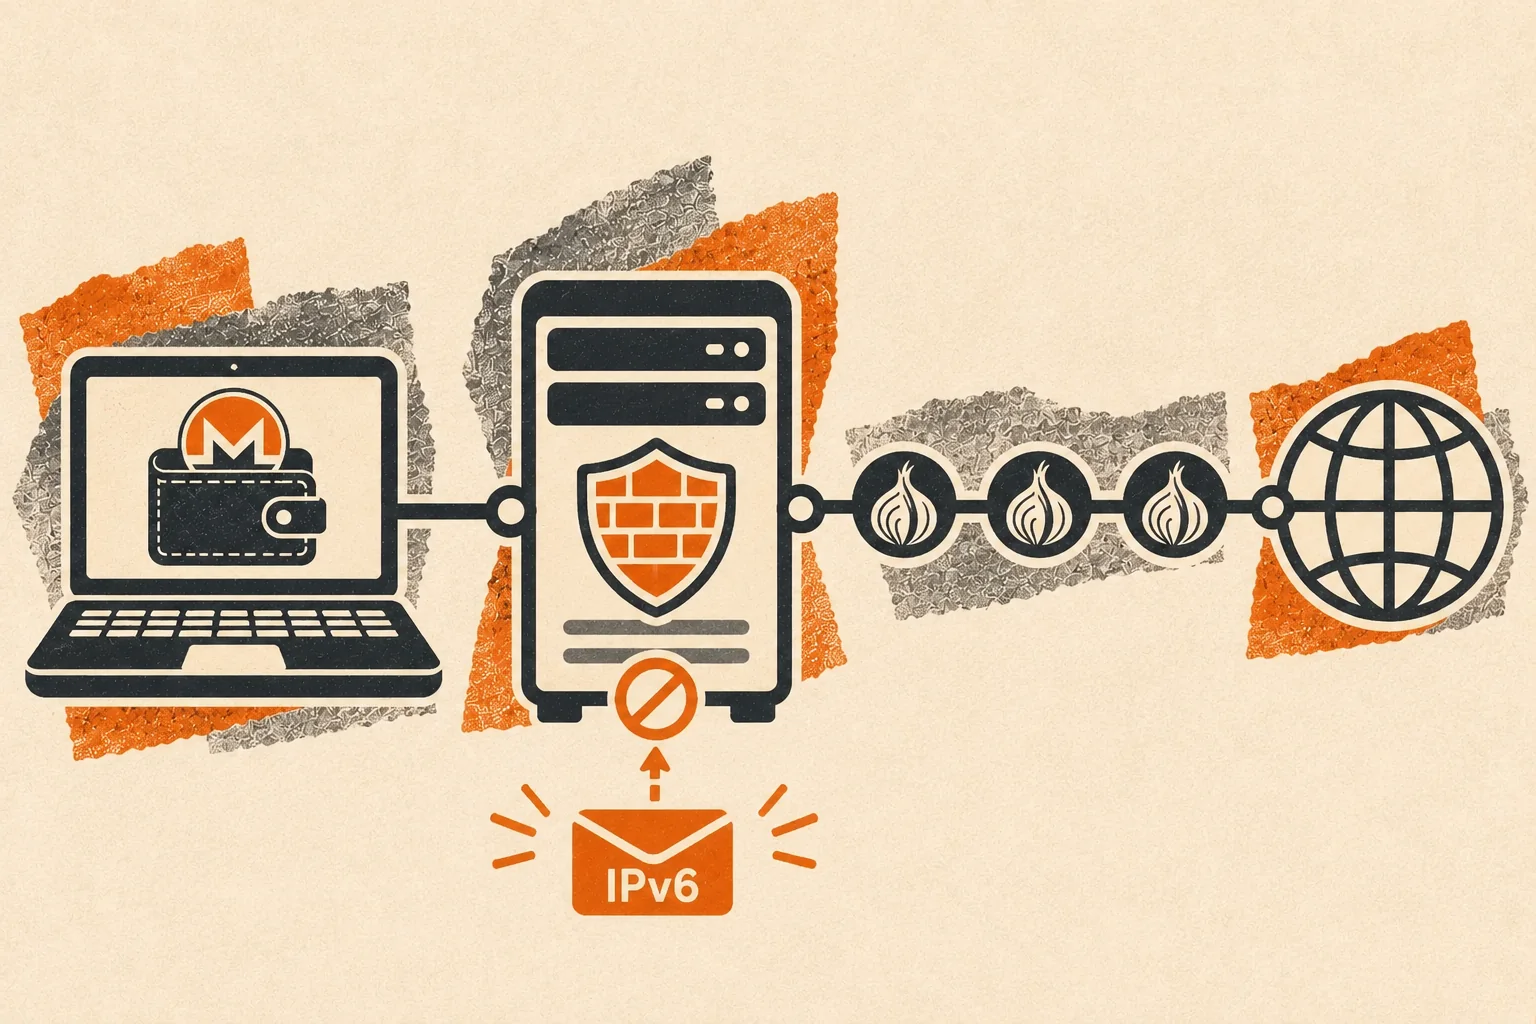
The patched Whonix IPv6 leak could let a compromised Whonix-Workstation make its Gateway send traffic outside Tor. The Whonix 18.2.4.2 announcement, published on October 24, 2026, identifies the affected scope as non-Qubes Whonix and credits researcher viajred. The stable repository offered fixed firewall packages from October 5.
For people using Whonix with a Monero wallet, the concern is network identity. The disclosure neither demonstrates a failure of Monero's cryptography nor establishes a wallet compromise.
How Whonix separates applications from Tor
Whonix uses two separate systems. Whonix-Workstation runs applications, while Whonix-Gateway handles their network access through Tor. The Workstation connects to the Gateway over an internal network instead of having its own direct internet connection.
Whonix relies on this separation to protect a user's network address even when an application behaves maliciously. The Gateway's firewall must enforce it. Compromising the Workstation should not give an attacker an ordinary connection to an internet server that can see the user's originating address.
How forged IPv6 addresses could bypass Tor
A packet's source address says where it came from. Malicious software can falsify that field. A firewall needs to check whether the claimed source makes sense for the interface receiving it.
The initial firewall change describes the Gateway receiving a forged-source packet from the Workstation and redirecting it toward Tor. The resulting reply could leave through the Gateway's external interface as non-Tor traffic. This is a specific response-path problem, rather than evidence that every application connection escaped Tor.
In the researcher-maintainer discussion, viajred described root-level malware on the Workstation as enough to trigger a clearnet packet. This assumes an already compromised Workstation. The report does not claim that an arbitrary website could expose every Whonix visitor without first compromising that environment.
Which Whonix users were affected?
The release announcement names non-Qubes Whonix. The researcher reports testing VirtualBox and says the fix stopped the proof of concept. A complete list of vulnerable image versions and separate test results for each platform remain unavailable.
The announced scope does not identify Qubes-Whonix as affected. Its Qubes integration uses a different virtualization and networking arrangement. This disclosure also supplies no evidence of a Tails vulnerability. Qubes users should also review the separately disclosed Qubes Xen isolation vulnerabilities.
What changed in whonix-firewall?
Whonix added reverse-path checks using nftables, Linux's packet-filtering framework. The release explains that IPv6 lacks the kernel equivalent of IPv4's rp_filter protection. The new rules reject packets whose claimed source does not have a matching return route through the incoming interface.
The first tagged package containing the initial check is 3:19.4-1, as identified in its changelog. Version 3:19.5-1 also includes a follow-up covering the internal tunnel interface.
The stable package repository supplies 3:19.5-1 as of November 5. Use the current stable update rather than treating the first code change as the complete maintenance target. October 5 marks the announced stable-package fix, while October 24 marks the 18.2.4.2 image announcement.
Update both systems and check the installed package
Follow Whonix's documented update command in both Gateway and Workstation:
upgrade-nonroot
Let each update finish and resolve any reported errors. On the Gateway, check the firewall package:
apt policy whonix-firewall
Read the Installed line, not only Candidate. At this review date, the current stable package is 3:19.5-1. An older installed version needs attention even if APT lists a newer candidate. Stay with the stable repository for this fix.
After updating, reboot both virtual machines to start them with the updated software and firewall configuration. An installed version alone does not prove which rules an already running system has loaded.
Whonix maintainers explain that ordinary package updates deliver point-release changes. A displayed image build number can remain unchanged after those updates. Moving between point releases does not require the major-version release-upgrade command.
Unanswered questions about the Whonix IPv6 leak
The official announcement and discussion do not list a CVE identifier or report confirmed exploitation in the wild. The thread records initial maintainer uncertainty, followed by the researcher's report that the fix blocked the attack on VirtualBox and the later security-fix announcement. That sequence supports reporting a disclosed, patched issue without inventing an exploitation history.
The same release separately fixes a local privilege-escalation issue in legacy-dist. Nothing in the cited disclosure establishes a combined attack involving both bugs.
For Monero users, keep network privacy separate from wallet and blockchain security. As our wallet connection guide explains, connection metadata matters even when private keys remain local. Updating Whonix addresses this network-isolation defect. It cannot establish whether an already compromised Workstation is trustworthy.